NO.31 Review the configuration below.
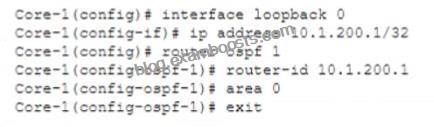
Why would you configure OSPF to use the IP address 10.1.200.1 as the router ID?
Explanation
The reason why you would configure OSPF Open Shortest Path First (OSPF) is a link-state routing protocol that dynamically calculates the best routes for data transmission within an IP network. OSPF uses a hierarchical structure that divides a network into areas and assigns each router an identifier called router ID (RID). OSPF uses hello packets to discover neighbors and exchange routing information. OSPF uses Dijkstra’s algorithm to compute the shortest path tree (SPT) based on link costs and build a routing table based on SPT. OSPF supports multiple equal-cost paths, load balancing, authentication, and various network types such as broadcast, point-to-point, point-to-multipoint, non-broadcast multi-access (NBMA), etc. OSPF is defined in RFC 2328 for IPv4 and RFC 5340 for IPv6. to use the IP address IP address Internet Protocol (IP) address is a numerical label assigned to each device connected to a computer network that uses the Internet Protocol for communication. An IP address serves two main functions: host or network interface identification and location addressing. There are two versions of IP addresses: IPv4 and IPv6. IPv4 addresses are 32 bits long and written in dotted-decimal notation, such as 192.168.1.1. IPv6 addresses are 128 bits long and written in hexadecimal notation, such as 2001:db8::1. IP addresses can be either static (fixed) or dynamic (assigned by a DHCP server). 10.1.200.1 as the router ID Router ID (RID) Router ID (RID) is a unique identifier assigned to each router in a routing domain or protocol. RIDs are used by routing protocols such as OSPF, IS-IS, EIGRP, BGP, etc., to identify neighbors, exchange routing information, elect designated routers (DRs), etc.
RIDs are usually derived from one of the IP addresses configured on the router’s interfaces or loopbacks, or manually specified by network administrators. RIDs must be unique within a routing domain or protocol instance. is that the loopback interface state Loopback interface Loopback interface is a virtual interface on a router that does not correspond to any physical port or connection. Loopback interfaces are used for various purposes such as testing network connectivity, providing stable router IDs for routing protocols, providing management access to routers, etc. Loopback interfaces have some advantages over physical interfaces such as being always up unless administratively shut down, being independent of any hardware failures or link failures, being able to assign any IP address regardless of subnetting constraints, etc. Loopback interfaces are usually numbered from zero (e.g., loopback0) upwards on routers. Loopback interfaces can also be created on PCs or servers for testing or configuration purposes using special IP addresses reserved for loopback testing (e.g., 127.x.x.x for IPv4 or ::1 for IPv6). Loopback interfaces are also known as virtual interfaces or dummy interfaces . Loopback interface state Loopback interface state refers to whether a loopback interface is up or down on a router . A loopback interface state can be either administratively controlled (by using commands such as no shutdown or shutdown ) or automatically determined by routing protocols (by using commands such as passive-interface or ip ospf network point-to-point ). A loopback interface state affects how routing protocols use the IP address assigned to the loopback interface for neighbor discovery , router ID selection , route advertisement , etc . A loopback interface state can also affect how other devices can access or ping the loopback interface . A loopback interface state can be checked by using commands such as show ip interfacebrief or show ip ospf neighbor . is independent of any physical interface and reduces routing updates.
The loopback interface state is independent of any physical interface because it does not depend on any hardware or link status. This means that the loopback interface state will always be up unless it is manually shut down by an administrator. This also means that the loopback interface state will not change due to any physical failures or link failures that may affect other interfaces on the router.
The loopback interface state reduces routing updates because it provides a stable router ID for OSPF that does not change due to any physical failures or link failures that may affect other interfaces on the router. This means that OSPF will not have to re-elect DRs Designated Routers (DRs) Designated Routers (DRs) are routers that are elected by OSPF routers in a broadcast or non-broadcast multi-access (NBMA) network to act as leaders and coordinators of OSPF operations in that network. DRs are responsible for generating link-state advertisements (LSAs) for the entire network segment, maintaining adjacencies with all other routers in the segment, and exchanging routing information with other DRs in different segments through backup designated routers (BDRs). DRs are elected based on their router priority values and router IDs . The highest priority router becomes the DR and the second highest priority router becomes the BDR . If there is a tie in priority values , then the highest router ID wins . DRs can be manually configured by setting the router priority value to 0 (which means ineligible) or 255 (which means always eligible) on specific interfaces . DRs can also be influenced by using commands such as ip ospf priority , ip ospf dr-delay , ip ospf network point-to-multipoint , etc . DRs can be verified by using commands such as show ip ospf neighbor , show ip ospf interface , show ip ospf database , etc . , recalculate SPT Shortest Path Tree (SPT) Shortest Path Tree (SPT) is a data structure that represents the shortest paths from a source node to all other nodes in a graph or network . SPT is used by link-state routing protocols such as OSPF and IS-IS to compute optimal routes based on link costs . SPT is built using Dijkstra’s algorithm , which starts from the source node and iteratively adds nodes with the lowest cost paths to the tree until all nodes are included . SPT can be represented by a set of pointers from each node to its parent node in the tree , or by a set of next-hop addresses from each node to its destination node in the network . SPT can be updated by adding or removing nodes or links , or by changing link costs . SPT can be verified by using commands such as show ip route , show ip ospf database , show clns route , show clns database , etc . , or send LSAs Link-State Advertisements (LSAs) Link-State Advertisements (LSAs) are packets that contain information about the state and cost of links in a network segment . LSAs are generated and flooded by link-state routing protocols such as OSPF and IS-IS to exchange routing information with other routers in the same area or level . LSAs are used to build link-state databases (LSDBs) on each router , which store the complete topology of the network segment . LSAs are also used to compute shortest path trees (SPTs) on each router , which determine the optimal routes to all destinations in the network . LSAs have different types depending on their origin and scope , such as router LSAs , network LSAs , summary LSAs , external LSAs , etc . LSAs have different formats depending ontheir type and protocol version , but they usually contain fields such as LSA header , LSA type , LSA length , LSA age , LSA sequence number , LSA checksum , LSA body , etc . LSAs can be verified by using commands such as show ip ospf database , show clns database , debug ip ospf hello , debug clns hello , etc . due to changes in router IDs.
The other options are not reasons because:
The IP address associated with the loopback interface is non-routable and prevents loops: This option is false because the IP address associated with the loopback interface is routable and does not prevent loops. The IP address associated with the loopback interface can be any valid IP address that belongs to an existing subnet or a new subnet created specifically for loopbacks. The IP address associated with the loopback interface does not prevent loops because loops are caused by misconfigurations or failures in routing protocols or devices, not by IP addresses.
The loopback interface state is dependent on the management interface state and reduces routing updates: This option is false because the loopback interface state is independent of any physical interface state, including the management interface state Management interface Management interface is an interface on a device that provides access to management functions such as configuration, monitoring, troubleshooting, etc . Management interfaces can be physical ports such as console ports, Ethernet ports, USB ports, etc., or virtual ports such as Telnet sessions, SSH sessions, web sessions, etc . Management interfaces can use different protocols such as CLI Command-Line Interface (CLI) Command-Line Interface (CLI) is an interactive text-based user interface that allows users to communicate with devices using commands typed on a keyboard . CLI is one of the methods for accessing management functions on devices such as routers, switches, firewalls, servers, etc . CLI can use different protocols such as console port serial communication protocol Serial communication protocol Serial communication protocol is a method of transmitting data between devices using serial ports and cables . Serial communication protocol uses binary signals that represent bits (0s and 1s) and sends them one after another over a single wire . Serial communication protocol has advantages such as simplicity, low cost, long
NO.33 You need to configure wireless access for several classes of loT devices, some of which operate only with 802
11b. Each class must have a unique PSK and will require a different security policy applied as a role There will be 15-20 different classes of devices and performance should be optimized Which option fulfills these requirements”
Explanation
The option that fulfills the requirements is to create individual SSIDs with unique PSK for each loT class, using 2.4 GHz and 5 GHz band. This option provides the following benefits:
Each loT class has a unique PSK that can be used to apply a different security policy as a role. This enhances the security and flexibility of the WLAN network.
Individual SSIDs allow for better isolation and management of different loT classes. This improves the performance and scalability of the WLAN network.
Using both 2.4 GHz and 5 GHz bands allows for backward compatibility with loT devices that operate only with 802.11b, which uses the 2.4 GHz band . It also allows for higher throughput and less interference for loT devices that support 802.11a, 802.11g, 802.11n, or 802.11ac, which use the 5 GHz band2.
The other options do not fulfill the requirements because:
Single SSID with MPSK for each loT class using 5 GHz and 6 GHz bands: This option does not support loT devices that operate only with 802.11b, which uses the 2.4 GHz band . It also does not optimize the performance of the WLAN network, as a single SSID may cause co-channel interference and congestion among different loT classes.
Single SSID with MPSK for each loT class using 2.4 GHz and 5 GHz bands: This option does not optimize the performance of the WLAN network, as a single SSID may cause co-channel interference and congestion among different loT classes.
Individual SSIDs with unique PSK for each loT class, using 5 GHz and 6 GHz bands: This option does not support loT devices that operate only with 802.11b, which uses the 2.4 GHz band1.
References: 1 https://en.wikipedia.org/wiki/IEEE_802.11b-1999 2
https://www.lifewire.com/wireless-standards-802-11a-802-11b-g-n-and-802-11ac-816553
NO.35 What is the ideal Aruba access switch for a cost-effective connection to 200-380 clients, printers and APs per distribution rack?
Explanation
The ideal Aruba access switch for a cost-effective connection to 200-380 clients, printers and APs per distribution rack is the Aruba CX 6200. This switch series is a cloud-manageable, stackable access switch series that is ideal for enterprise branch offices and campus networks, as well as SMBs. The CX 6200 series offers the following benefits:
Enterprise-class connectivity: The CX 6200 series supports ACLs, robust QoS, and common protocols such as static and Access OSPF routing.
Power and speed for users and IoT: The CX 6200 series provides built-in 1/10GbE uplinks and 30W to
60W of Class 4 to Class 6 PoE for powering devices such as APs and cameras.
Scalable growth made simple: The CX 6200 series supports Aruba Virtual Switching Framework (VSF) that allows you to quickly grow your network to eight members in a single stack using high-performance built-in 10G SFP ports.
Management flexibility: The CX 6200 series supports a choice of management, including cloud-based and on-prem Central, CLI, switch Web GUI and programmability with AOS-CX operating system, and REST APIs.
The other options are not ideal because:
Aruba CX 6400: This switch series is a high-availability modular switch series that is ideal for versatile edge access to data center deployments. It offers more performance, scalability, and modularity than the CX 6200 series, but it is also more expensive and complex to deploy and manage. It may not be cost-effective for connecting 200-380 clients per distribution rack.
Aruba CX 6300: This switch series is a layer 3 stackable access and aggregation switch series that offers Smart Rate and High Power PoE. It offers more features and performance than the CX 6200 series, but it is also more expensive and may not be necessary for connecting 200-380 clients per distribution rack.
Aruba CX 6000: This switch series is a layer 2 access switch series that offers PoE. It offers less features and performance than the CX 6200 series, and it does not support VSF stacking or routing protocols. It may not be sufficient for connecting 200-380 clients per distribution rack.
References: https://www.arubanetworks.com/products/switches/access/
https://www.arubanetworks.com/products/switches/access/6200-series/
https://www.arubanetworks.com/products/switches/access/6400-series/
https://www.arubanetworks.com/products/switches/access/6300-series/
https://www.arubanetworks.com/products/switches/access/6000-series/
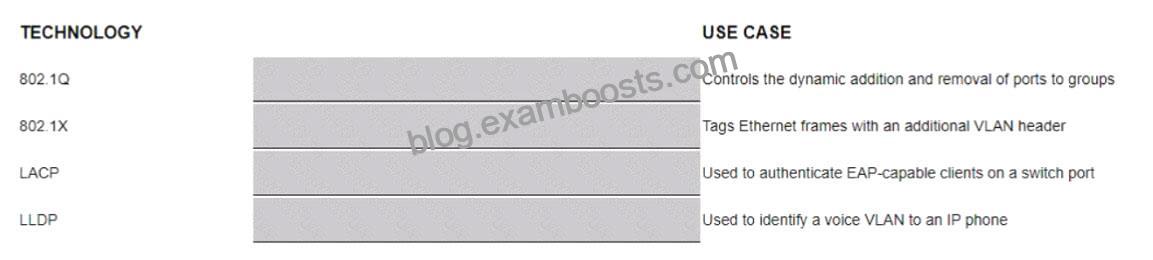
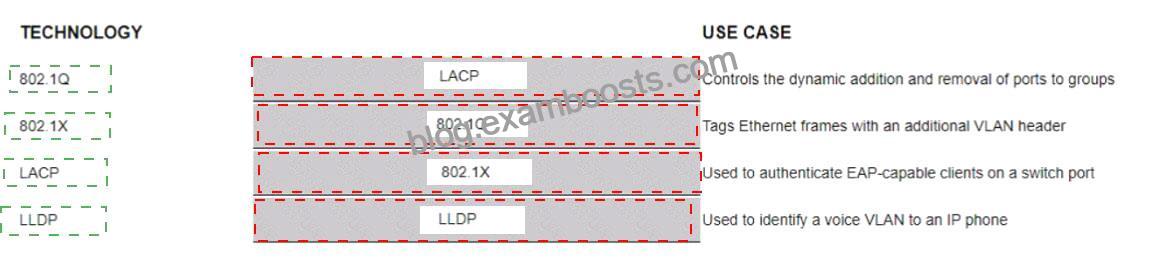
NO.36 Match the switching technology with the appropriate use case.
Explanation
USE CASE: a) Controls the dynamic addition and removal of ports to groups Technology: 3) LACP USE CASE: b) Tags Ethernet frames with an additional VLAN header Technology: 1) 802.1Q USE CASE: c) Used to authenticate EAP-Capable client on a switch port Technology: 2) 802.1X USE CASE: d) Used to identify a voice VLAN to an IP phone Technology: 4) LLDP The following table summarizes the switching technologies and their use cases:
Technology
Use case
1) 802.1Q
802.1Q is a standard that defines how to create and manage virtual LANs (VLANs) on a network. VLANs allow network administrators to logically segment a network into different broadcast domains, improving security, performance, and manageability. 802.1Q tags Ethernet frames with an additional VLAN header that contains a VLAN identifier (VID), which indicates which VLAN the frame belongs to1.
2) 802.1X
802.1X is a standard that defines how to provide port-based network access control (PNAC) on a network.
PNAC allows network administrators to authenticate and authorize devices before granting them access to network resources. 802.1X uses the Extensible Authentication Protocol (EAP) to exchange authentication messages between a supplicant (a device that wants to access the network), an authenticator (a device that controls access to the network, such as a switch), and an authentication server (a device that verifies the credentials of the supplicant, such as a RADIUS server)
3) LACP
LACP stands for Link Aggregation Control Protocol, which is part of the IEEE 802.3ad standard that defines how to bundle multiple physical links into a single logical link, also known as a link aggregation group (LAG) or an EtherChannel. LAGs provide increased bandwidth, load balancing, and redundancy for network connections. LACP controls the dynamic addition and removal of ports to groups, ensuring that only ports with compatible configurations can form a LAG3.
4) LLDP
LLDP stands for Link Layer Discovery Protocol, which is part of the IEEE 802.1AB standard that defines how to discover and advertise information about neighboring devices on a network. LLDP operates at Layer 2 of the OSI model and uses TLVs (type-length-value) to exchange information such as device name, port number, VLAN ID, capabilities, and power requirements. LLDP can be used to identify a voice VLAN to an IP phone by sending a TLV that contains the voice VLAN ID and priority.
References: 1 https://en.wikipedia.org/wiki/IEEE_802.1Q 2 https://en.wikipedia.org/wiki/IEEE_802.1X 3
https://en.wikipedia.org/wiki/Link_aggregation
https://en.wikipedia.org/wiki/Link_Layer_Discovery_Protocol
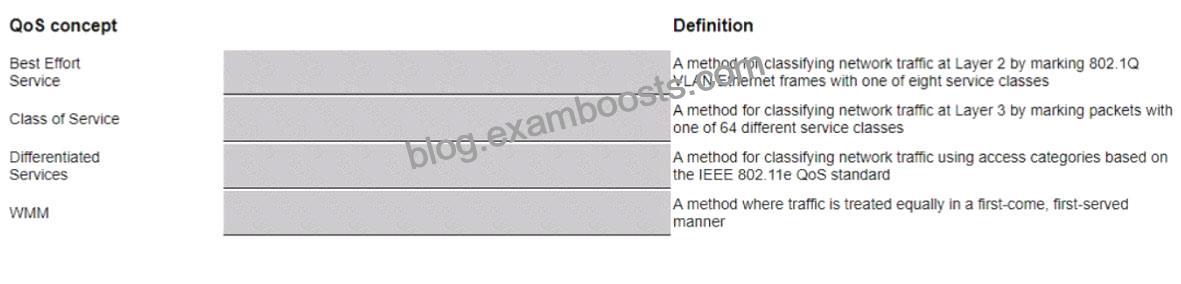
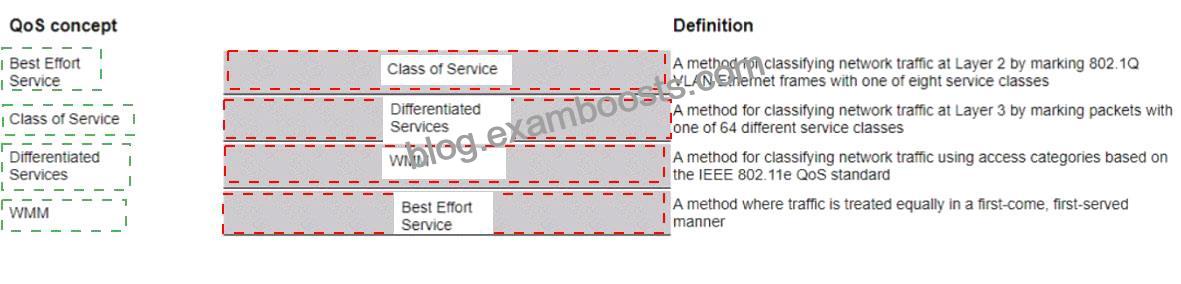
NO.37 Match the appropriate QoS concept with its definition.
Explanation
QoS Quality of Service (QoS) is a set of techniques that manage network resources and provide different levels of service to different types of traffic based on their requirements. QoS can improve network performance, reduce latency, increase throughput, and prevent congestion. concept and its definition. Here is my answer:
QoS Concept:
Best Effort Service
Class of Service
Differentiated Services
WMM ====================== Definition:
d) A method where traffic is treated equally in a first-come, first-served manner a) A method for classifying network traffic at Layer 2 by marking 802.1Q VLAN Ethernet frames with one of eight service classes b) A method for classifying network traffic at Layer 3 by marking packets with one of 64 different service classes c) A method for classifying network traffic using access categories based on the IEEE 802.11e QoS standard Short But Comprehensive Explanation of Correct Answer Only: The correct match between QoS concept and its definition is as follows:
Best Effort Service: This is a method where traffic is treated equally in a first-come, first-served manner without any prioritization or differentiation. This is the default service level for most networks and applications that do not have specific QoS requirements or guarantees. Best Effort Service does not provide any assurance of bandwidth, delay, jitter, or packet loss.
Class of Service: This is a method for classifying network traffic at Layer 2 by marking 802.1Q VLAN Ethernet frames with one of eight service classes (0 to 7). These service classes are also known as IEEE
802.1p priority values or PCP Priority Code Point (PCP) is a 3-bit field in the 802.1Q VLAN tag that indicates the priority level of an Ethernet frame . Class of Service allows network devices to identify and handle different types of traffic based on their priority levels. Class of Service is typically used in LAN Local Area Network (LAN) is a network that connects devices within a limited geographic area, such as a home, office, or building environments where Layer 2 switching is predominant.
Differentiated Services: This is a method for classifying network traffic at Layer 3 by marking packets with one of 64 different service classes (0 to 63). These service classes are also known as DiffServ Code Points (DSCP) DiffServ Code Point (DSCP) is a 6-bit field in the IP header that indicates the service class of a packet . Differentiated Services allows network devices to identify and handle different types of traffic based on their service classes. Differentiated Services is typically used in WAN Wide Area Network (WAN) is a network that connects devices across a large geographic area, such as a country or continent environments where Layer 3 routing is predominant.
WMM: This is a method for classifying network traffic using access categories based on the IEEE
802.11e QoS standard. WMM stands for Wi-Fi Multimedia and it is a certification program developed by the Wi-Fi Alliance to enhance QoS for wireless networks. WMM defines four access categories (AC): Voice, Video, Best Effort, and Background. These access categories correspond to different priority levels and contention parameters for wireless traffic. WMM allows wireless devices to identify and handle different types of traffic based on their access categories.
References: https://en.wikipedia.org/wiki/Quality_of_service
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/qos_dfsrv/configuration/xe-16/qos-dfsrv-xe-16-book/qos-dfsr
https://www.cisco.com/c/en/us/support/docs/wireless-mobility/wireless-lan-wlan/81831-qos-wlan.html
https://www.wi-fi.org/discover-wi-fi/wi-fi-certified-wmm
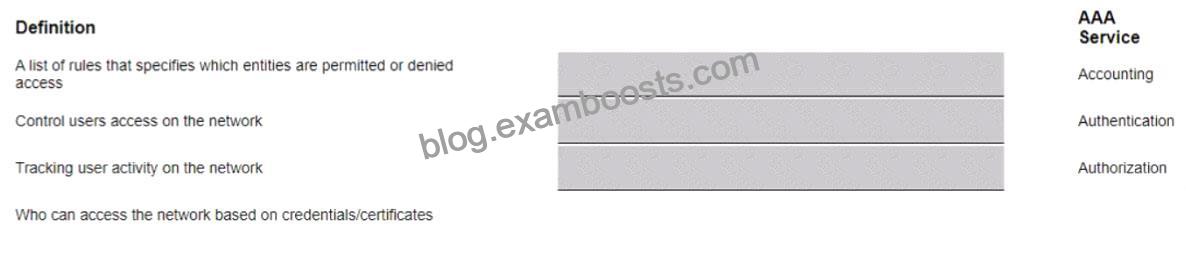
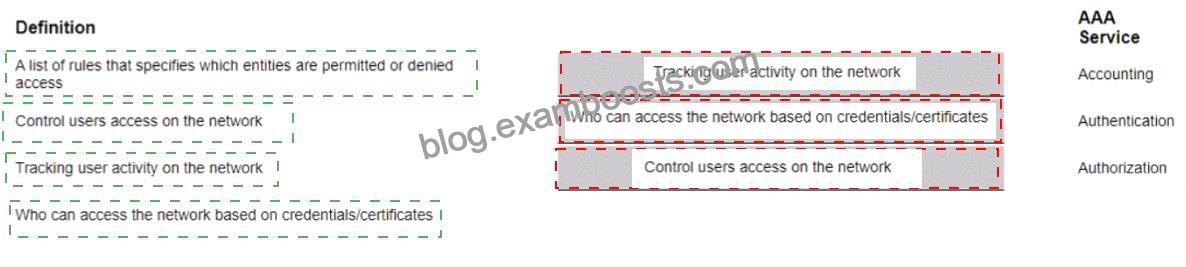
NO.38 Match each AAA service with its correct definition (Matches may be used more than once or not at all)
Explanation
AAA Authentication, Authorization, and Accounting (AAA) Authentication, Authorization, and Accounting (AAA) is a framework that provides security services for network access control . AAA consists of three components:
Authentication: The process of verifying the identity of a user or device that wants to access the network based on credentials such as username and password , certificates , tokens , etc . Authentication can use different protocols such as PAP , CHAP , EAP , RADIUS , TACACS+ , etc .
Authorization: The process of granting or denying access to network resources based on the identity and privileges of a user or device . Authorization can use different methods such as ACLs , RBAC , MAC , DAC , etc .
Accounting: The process of recording and reporting the activities and usage of network resources by users or devices . Accounting can use different formats such as syslog , SNMP , NetFlow , etc .
service. Here is my answer:
The correct match for each AAA service with its definition is:
Accounting: C. Tracking user activity on the network
Authentication: D. Who can access the network based on credentials/certificates Authorization: B. Control users access on the network The other options are not correct matches because:
A list of rules that specifies which entities are permitted or denied access: This option is a definition of an access control list (ACL) Access Control List (ACL) Access Control List (ACL) is a list of rules that specifies which entities are permitted or denied access to a network resource such as a router , switch , firewall , server , etc . ACLs can be based on different criteria such as source and destination IP addresses , port numbers , protocol types , time of day , etc . ACLs can be applied to different interfaces or directions such as inbound or outbound . ACLs can be verified by using commands such as show access-lists , show ip access-lists , debug ip packet , etc . , not an AAA service.
Who can access the network based on credentials/certificates: This option is a definition of authentication, not authorization. Authorization is the process of granting or denying access to network resources based on the identity and privileges of a user or device, not based on credentials/certificates.
References: https://en.wikipedia.org/wiki/AAA_(computer_security)
https://www.cisco.com/c/en/us/support/docs/security-vpn/remote-authentication-dial-user-service-radius/13838-1
NO.42 You need to troubleshoot an Aruba CX 6200 4-node VSF stack switch that fails to boot correctly Select the option that allows you to access the switch and see the boot options available for OS images and ServiceOS.
Explanation
The option that allows you to access the switch and see the boot options available for OS images and ServiceOS is Conductor USB-C console port. This option provides direct access to ServiceOS, which is an operating system that runs on Aruba CX switches independently of AOS-CX Aruba Operating System CX (AOS-CX) is an operating system that runs on Aruba CX switches . ServiceOS provides low-level functions such as booting, firmware upgrades, password recovery, hardware diagnostics, switch stacking, and system recovery. ServiceOS can be accessed through one of two methods:
Conductor USB-C console port: This method allows you to connect your PC or laptop to the USB-C console port on any member switch in a VSF stack using a USB-C cable. This method provides direct access to ServiceOS without requiring any configuration or authentication on AOS-CX.
AOS-CX CLI: This method allows you to access ServiceOS through AOS-CX CLI using SSH or Telnet protocols. This method requires you to configure an IP address on AOS-CX and authenticate with your username and password.
To see the boot options available for OS images and ServiceOS, you need to access ServiceOS through Conductor USB-C console port and enter boot menu command at ServiceOS prompt.
The other options do not allow you to access the switch and see the boot options available for OS images and ServiceOS because:
Member 2 RJ-45 console port: This option allows you to connect your PC or laptop to the RJ-45 console port on any member switch in a VSF stack using an RJ-45 cable. This option provides direct access to AOS-CX CLI, not ServiceOS.
Member 2 switch mgmt port: This option allows you to connect your PC or laptop to the switch mgmt port on any member switch in a VSF stack using an Ethernet cable. This option provides indirect access to AOS-CX CLI through SSH or Telnet protocols, not ServiceOS.
Conductor mgmt port using SSH: This option allows you to connect your PC or laptop to the mgmt port on any member switch in a VSF stack using an Ethernet cable. This option provides indirect access to AOS-CX CLI through SSH protocol, not ServiceOS.
References:
https://www.arubanetworks.com/techdocs/AOS-CX_10_08/NOSCG/Content/cx-noscg/serviceos/serviceos-overv
https://www.arubanetworks.com/techdocs/AOS-CX_10_08/NOSCG/Content/cx-noscg/serviceos/access-serviceo
https://www.arubanetworks.com/techdocs/AOS-CX_10_08/NOSCG/Content/cx-noscg/serviceos/boot-menu.htm
NO.43 Which part of the WPA Key Hierarchy is used to encrypt and/or decrypt data”
Explanation
The part of WPA Key Hierarchy that is used to encrypt and/or decrypt data is Pairwise Temporal Key (PTK).
PTK is a key that is derived from PMK Pairwise Master Key (PMK) is a key that is derived from PSK Pre-shared Key (PSK) is a key that is shared between two parties before communication begins , ANonce Authenticator Nonce (ANonce) is a random number generated by an authenticator (a device that controls access to network resources, such as an AP) , SNonce Supplicant Nonce (SNonce) is a randomnumber generated by supplicant (a device that wants to access network resources, such as an STA) , AA Authenticator Address (AA) is MAC address of authenticator , SA Supplicant Address (SA) is MAC address of supplicant using Pseudo-Random Function (PRF). PTK consists of four subkeys:
KCK Key Confirmation Key (KCK) is used for message integrity check
KEK Key Encryption Key (KEK) is used for encryption key distribution
TK Temporal Key (TK) is used for data encryption
MIC Message Integrity Code (MIC) key
The subkey that is specifically used for data encryption is TK Temporal Key (TK). TK is also known as Pairwise Transient Key (PTK). TK changes periodically during communication based on time or number of packets transmitted.
The other options are not part of WPA Key Hierarchy because:
PMK: PMK is not part of WPA Key Hierarchy, but rather an input for deriving PTK.
KCK: KCK is part of WPA Key Hierarchy, but it is not used for data encryption, but rather for message integrity check.
Nonce: Nonce is not part of WPA Key Hierarchy, but rather an input for deriving PTK.
References: https://en.wikipedia.org/wiki/Wi-Fi_Protected_Access#WPA_key_hierarchy_and_management
https://www.cwnp.com/wp-content/uploads/pdf/WPA2.pdf