[May-2024] MS-500 Exam Dumps, MS-500 Practice Test Questions [Q155-Q178]

[May-2024] MS-500 Exam Dumps, MS-500 Practice Test Questions [Q155-Q178]

May 14, 2024 MS-500 > Microsoft 0
Rate this post

[May-2024] MS-500 Exam Dumps, MS-500 Practice Test Questions

Attested MS-500 Dumps PDF Resource [2024]

QUESTION 155
You have a Microsoft 365 subscription that contains a user named User.

You enroll devices in Microsoft Intune as shown in the following table.
Each device has two line of business apps named App1 and App2 installed.

You create application control policies targeted to all the app types in Microsoft Endpoint Manager as shown in the following table.

For each of the following statements, Select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 156
Microsoft 365 E5 licenses. You plan to implement an Advanced Threat Protection (ATP) anti-phishing policy. You need to enable mailbox intelligence for all users. What should you do first?


QUESTION 157
You have a Microsoft 365 E5 tenant that contains three users named User1, User2, and User3.
You need to assign roles or role groups to the users as shown in the following table.

What should you use to assign a role or role group to each user? To answer, drag the appropriate tools to the correct roles or role groups. Each tool may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

QUESTION 158
You have a Microsoft 365 subscription for a company named Contoso, Ltd. All data is in Microsoft 365.
Contoso works with a partner company named Litware, Inc. Litware has a Microsoft 365 subscription.
You need to allow users at Contoso to share files from Microsoft OneDrive to specific users at Litware.
Which two actions should you perform from the OneDrive admin center? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.


QUESTION 159
You have a Microsoft 365 E5 subscription.
Some users are required to use an authenticator app to access Microsoft SharePoint Online.
You need to view which users have used an authenticator app to access SharePoint Online. The solution must minimize costs.
What should you do?


QUESTION 160
You have a Microsoft 365 subscription. From the Security & Compliance admin center, you create the retention policies shown in the following table.

Policy1 if configured as showing in the following exhibit.

Policy2 is configured as shown in the following exhibit.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

QUESTION 161
Your network contains an on-premises Active Directory domain. The domain contains the servers shown in the following table.

You plan to implement Microsoft Defender for Identity for the domain. You install a Microsoft Defender for Identity standalone sensor on Server 1. You need to monitor the domain by using Microsoft Defender for Identity. What should you do?


QUESTION 162
You configure Microsoft Azure Active Directory (Azure AD) Connect as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

QUESTION 163
You have a Microsoft 365 subscription.
A user reports that changes were made to several files in Microsoft OneDrive.
You need to identify which files were modified by which users in the user’s OneDrive.
What should you do?


QUESTION 164
Your company has a Microsoft 365 E5 subscription that contains a user named User.
User1 leaves the company.
You need to identify all the personal data of User1 that is stored in the subscription.
What should you do in the Microsoft Purview compliance portal?


QUESTION 165
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.

You enable Customer Lockbox.
Which users will be notified when a Microsoft support engineer requests access to the organization?


QUESTION 166
You have a Microsoft 365 tenant.
You create an attack surface reduction policy that uses an application control profile as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

QUESTION 167
You have a Microsoft 365 subscription.
You enable auditing for the subscription.
You plan to provide a user named Auditor with the ability to review audit logs.
You add Auditor to the Global administrator role group.
Several days later, you discover that Auditor disabled auditing.
You remove Auditor from the Global administrator role group and enable auditing.
* Be prevented from disabling auditing
* Use the principle of least privilege
* Be able to review the audit log
To which role group should you add Auditor?


QUESTION 168
You have a Microsoft 365 subscription that uses a default domain name of contoso.com.
The multi-factorauthentication (MFA) service settings are configured as shown in the exhibit. (Clock theExhibittab.)

In contoso.com, you create the users shown in the following table.

What is the effect of the configuration? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.

QUESTION 169
You have a Microsoft 365 subscription that contains the groups shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic NOTE: Each correct selection is worth one point.

QUESTION 170
You have a Microsoft 365 subscription that uses a default domain name of fabrikam.com.
You create a safe links policy, as shown in the following exhibit.

Which URL can a user safely access from Microsoft Word Online?


QUESTION 171
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.

You register devices in contoso.com as shown in the following table.

You create app protection policies in Intune as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 172
You have a Microsoft 365 tenant.
You create an attack surface reduction policy that uses an application control profile as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

QUESTION 173
You need to enable and configure Microsoft Defender ATP to meet the security requirements. What should you do?


QUESTION 174
You have a Microsoft 365 E5 subscription that contains 500 Windows 10 devices The subscription uses Microsoft Defender for Endpoint and is integrated with Microsoft Endpoint Manager. AJI the devices have Defender for Endpoint deployed.
You create a Conditional Access policy as shown in the following table.

You need to ensure that devices that have a machine risk score of high are blocked. What should you do in Microsoft Endpoint Manager?


QUESTION 175
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn’t matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308
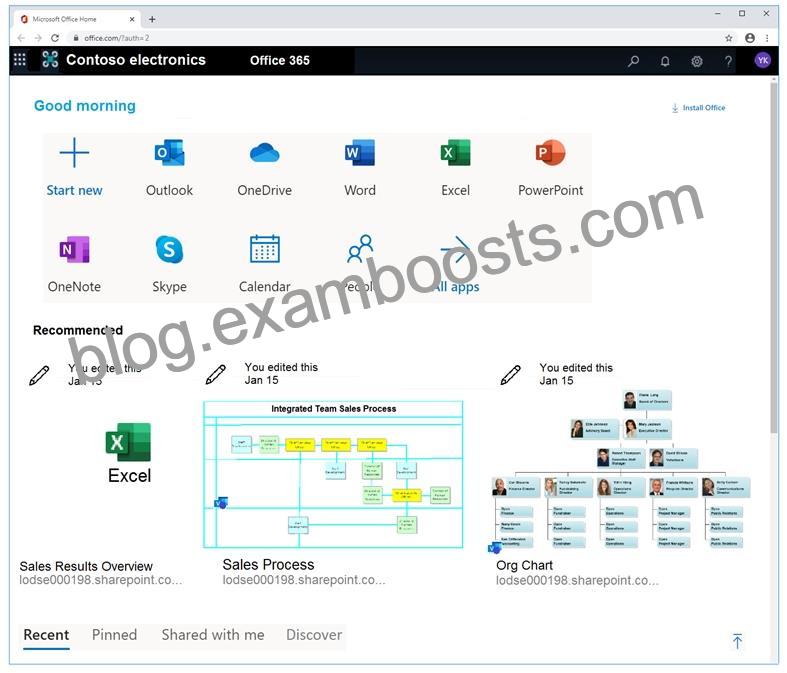
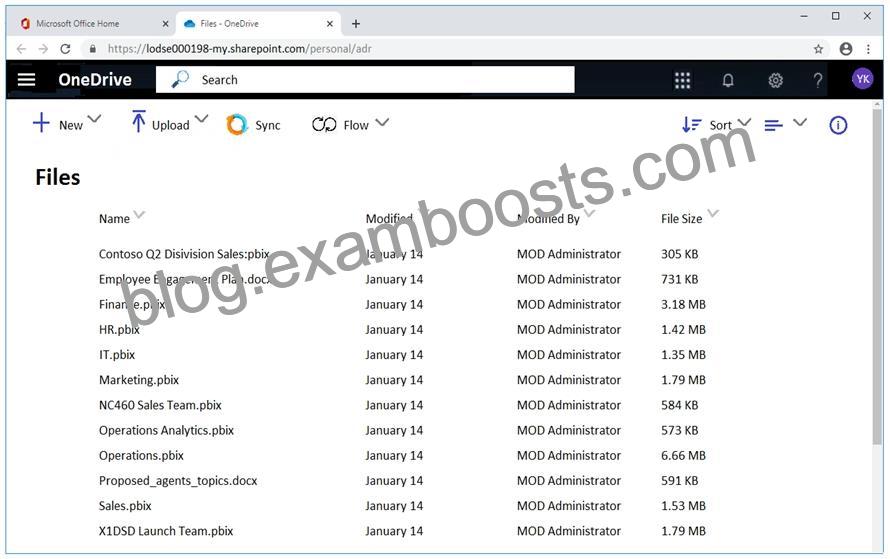
You need to ensure that all the email messages in the mailbox of a user named Allan Deyoung are retained for a period of 90 days, even if the messages are deleted.
To complete this task, sign in to the Microsoft 365 admin center.

QUESTION 176
You need to implement a solution to manage when users select links in documents or email messages from Microsoft Office 365 ProPlus applications or Android devices. The solution must meet the following requirements:
* Block access to a domain named fabrikam.com
* Store information when the users select links to fabrikam.com
To complete this task, sign in to the Microsoft 365 portal.

QUESTION 177
You have an Azure Sentinel workspace.
You configure a rule to generate Azure Sentinel alerts when Azure Active Directory (Azure AD) Identity Protection detects risky sign-ins. You develop an Azure Logic Apps solution to contact users and verify whether reported risky sign-ins are legitimate.
You need to configure the workspace to meet the following requirements:
Call the Azure logic app when an alert is triggered for a risky sign-in.
To the Azure Sentinel portal, add a custom dashboard that displays statistics for risky sign-ins that are detected and resolved.
What should you configure in Azure Sentinel to meet each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 178
You are evaluating which devices are compliant in Intune.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.


Latest MS-500 Actual Free Exam Questions Updated 329 Questions: https://www.examboosts.com/Microsoft/MS-500-practice-exam-dumps.html


Related Links: www.stes.tyc.edu.tw www.fanart-central.net www.stes.tyc.edu.tw www.stes.tyc.edu.tw fortunetelleroracle.com www.stes.tyc.edu.tw


Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below